리더, 감사인, 이사회가 실제로 쓸 수 있는 증거.
Every verification run, policy evaluation, approval, and outcome is recorded as durable evidence, exportable for release reviews, compliance packs, and executive readouts.
PROVENANCE
Who, what, why
Every decision attributable to policy and a named approver.
감사 대비
컴플라이언스 팩
- SOC 2
- ISO
- 증적 추적.
주기
예약됨
설정한 일정에 따라 자동으로 생성됩니다.

직면한 과제
보안 테스트가 지속적이지 않고 주기적으로 이루어집니다
보안 테스트가 지속적이지 않고 주기적으로 이루어집니다
규정 준수 감사에 수동 증빙 수집이 필요합니다
규정 준수 감사에 수동 증빙 수집이 필요합니다
새로운 취약점이 프로덕션에서 발견됩니다
새로운 취약점이 프로덕션에서 발견됩니다
보안 팀과 개발 팀의 방향이 어긋나 있습니다
보안 팀과 개발 팀의 방향이 어긋나 있습니다
Zof가 돕는 방법
지속적 보안 테스트
모든 변경에 대해 OWASP 및 취약점 스캔을 수행합니다.
규정 준수 자동화
SOC2, HIPAA, GDPR, PCI-DSS 통제 항목의 자동화된 검증.
증빙 수집
감사 대비가 완료된 규정 준수 보고서를 자동으로 생성합니다.
시프트 레프트 보안
보안 테스트를 개발 워크플로에 통합하세요.
핵심 기능
✓
OWASP Top 10 스캔
✓
규정 준수 통제 검증
✓
감사 보고서 생성
✓
취약점 추적
✓
보안 기준선 시행
✓
리스크 평가
Related sessions
Sessions from the Zof media library relevant to this topic.
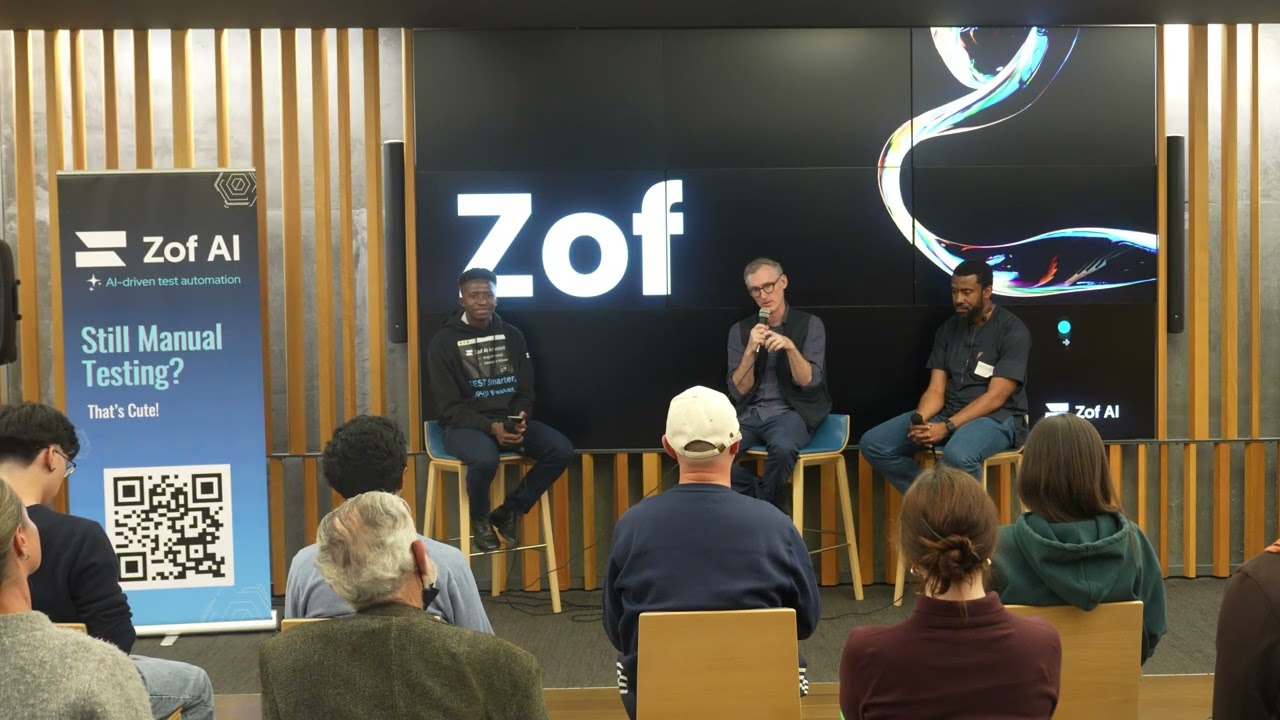 13:03Executive EventsZof Event Hosted by CBRE
How Quality Intelligence Is Replacing Traditional QA
Executive highlights from the Zof event hosted by CBRE on how quality intelligence platforms replace reactive QA with governed autonomous reliability, System Graph context, and evidence-based validation across enterprise software delivery.
Watch session 13:53Executive EventsQuality at Scale Event
Scaling Quality and Security in the AI Era
Fireside recap with Patrick Ayertey on scaling quality and security for enterprise engineering teams, covering AI risk, defense in depth, continuous verification, and human-authorized remediation at scale.
Watch session